

Threat Horizons 2026–2027: what we saw, and what comes next
What JODOR sensors recorded inside Saudi Arabia, what the main global and regional studies found in 2026, and five things we expect in 2027.
Download the report (PDF)Plain-language reading for leaders, technical detail for defenders, and short videos for everyone in between.
Reports and articles
What JODOR sensors recorded inside Saudi Arabia, what the main global and regional studies found in 2026, and five things we expect in 2027.
Download the report (PDF)Half the attackers JODOR recorded were on no public blocklist. This article explains why deception finds them, and how you can receive a list of your own attackers without installing anything.
Download the report (PDF)A technical read of 2,207 attackers over 56 days: timing, exploit families and CVEs, MITRE ATT&CK techniques, and the YARA rules JODOR uses to catch them.
Download the report (PDF)How the system is built, how each alert moves from a fixed rule to a fast model, an expert model and finally a person, and what the numbers showed after 15 days of live operation.
Download the report (PDF)Articles & research
What JODOR sensors recorded inside Saudi Arabia, what the main global and regional studies found in 2026, and five things we expect in 2027.
Videos
Attacks don’t wait for anyone. See how our three service lines and JODR aMDR work together to keep you ahead.
 More videos coming soon
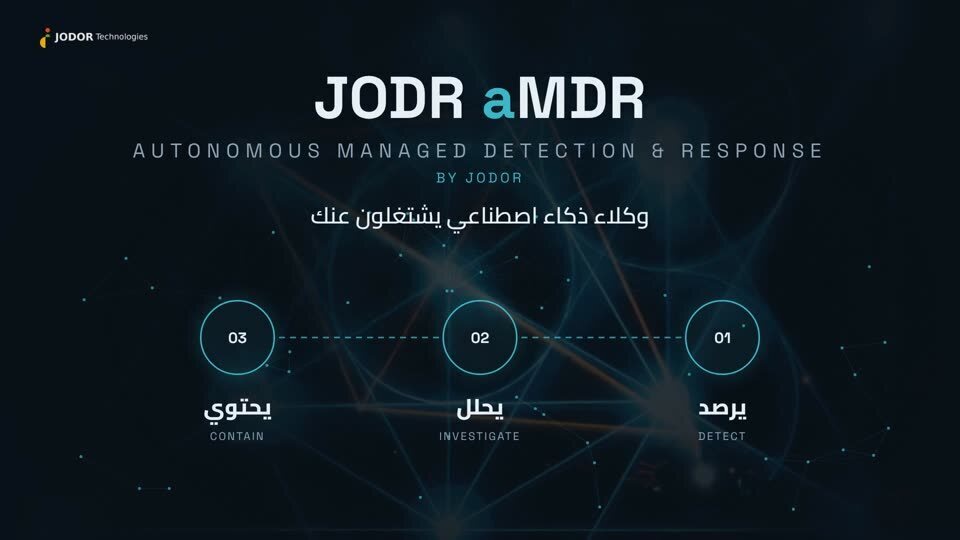 More videos coming soon
Your payment processor, cloud provider, outsourced developers, call centre: each one either connects to your systems or holds part of your data. So a gap on their side is really a gap on yours. Getting third-party risk right doesn't have to be complicated: ▪ Tier your suppliers by the data and access they hold. They don't all carry the same risk. ▪ Put security requirements in the contract from da
Many organisations treat customer data as something to collect and keep. The Personal Data Protection Law (PDPL) asks for something different: know exactly what personal data you hold, why you collected it, who can reach it, and how long you'll keep it. In practice, readiness comes down to four steps: ▪ Start by mapping where personal data is collected, where it's stored and who it's shared with.
: 1. What are our top five cyber risks, described in business terms? 2. Which regulatory requirements are we not yet meeting, and when will we? 3. How quickly would we know about a serious incident? 4. Who outside the organisation holds our sensitive data? 5. Is our security spend aligned with the risks that matter most? #JODORTechnologies #JODORChecklist #GRC #Cybersecurity
Passing an assessment is the floor, not the ceiling. Good governance tells leadership where the real risk sits and what to do about it next. Our GRC practice helps institutions: ▪ Assess maturity against NCA ECC, SAMA CSF and PDPL ▪ Build policies and standards people can actually follow ▪ Run a living risk register, not an annual spreadsheet ▪ Report cyber risk to the board in business terms The
Saudi regulated institutions answer to clear frameworks: NCA ECC, SAMA CSF, PDPL, and often ISO/IEC 27001 alongside them. Yet many security programmes still produce findings that have to be re-mapped by hand before every review. Our approach is simple: every assessment, design and deliverable is mapped to the framework from day one. When the auditor asks "which control does this satisfy?", the ans
Our Cybersecurity Consulting & Delivery line is organised around five disciplines: 01 Governance, Risk & Compliance 02 Offensive Security 03 Cyber Defence 04 Cloud & AI Security 05 Security Architecture Each discipline has its own specialists and methods, but they share one delivery standard, one reporting format and one rule: every finding is traceable to the framework you are measured against. O
Why traditional VPN falls short, how Zero Trust Network Access works, and a migration roadmap aligned with NCA ECC, NIST and CISA guidance.
Explore the whitepaperOne email when something new is published. Nothing else.